Apple Updates Anti-Malware Definitions to Address Fake Flash Player Trojan
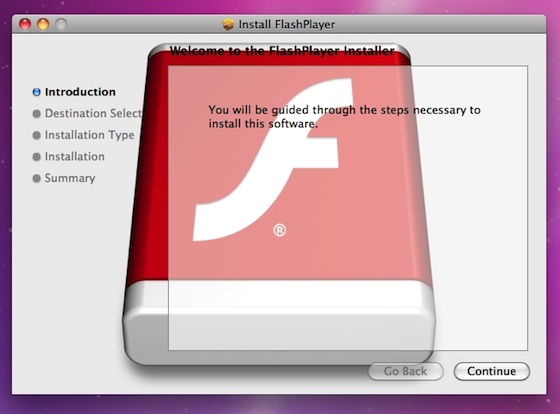
Fake Flash Player trojan installer
While things have been relatively quiet on the malware front for OS X since a raid on Russian payment processing firm ChronoPay appeared to have taken down MacDefender nearly two months ago, one new trojan horse did pop up earlier this month. As detailed by F-Secure, the trojan known as "OSX.QHost.WB.A" masquerades as a Flash Player installer but actually adds entries to a computer's hosts file to redirect users attempting to visit certain Google sites.
Once installed, the trojan adds entries to the hosts file to hijack users visiting various Google sites (e.g., Google.com.tw, Google.com.tl, et cetera) to the IP address 91.224.160.26, which is located in Netherlands.
The server at the IP address displays a fake webpage designed to appear similar to the legitimate Google site.

Consequently, Apple earlier this week made its first significant addition to its "XProtect.plist" file since the spate of MacDefender variants surfaced in June. The XProtect.plist file contains malware definitions to enable users' systems to recognize and warn users of malicious downloads, a feature that debuted with Mac OS X Snow Leopard back in 2009.
The original anti-malware system required manual updates to account for new threats, and as such was updated only rarely by Apple as part of larger software updates. But with an Apple software update issued in response to the MacDefender threat earlier this year, Mac OS X systems are now able to make daily checks for updates to that file to ensure up-to-date protection against malware.
Top Rated Comments
(View all)And yes, this is not a virus. This is malware.
A question I have though, is under what conditions should ANY software modify the hosts file? Should Apple even allow programs that have been granted administrative rights to alter the hosts file? There is only a very limited benvolent use case for such an action, and that very related to what they did here: some anti-ad or anti-spyware utilities modify a host file to redirect known ad-producing domains to a "safe" domain. I personally think any modification of the host file should be given a warning like this:
The program _____ is trying to update a core Mac OS X system file that is used to provide network connectivity. While online advertisement blocking programs may require legitimate use of this file, most others applications may represent an attempt to install malicious software onto your computer. Are you sure you want to allow program _____ to modify this file?
That's why you need to disable flash. :p
This has nothing to do with Flash.
Funny.... I updated Flash yesterday on my kids' Mac mini and I thought that writing a Trojan that masquerades as an update to Flash would be brilliant since Flash is updated so often and getting prompted that you need to update Flash to view a website is very common..... And then today, here it is.
Hmm, what are you thinking about today?
So this trojan, doesn't prompt you like a normal update correct? Cause there was a normal update for flash that was found threw software update. Or was that the trojan? The reason i ask is because I'm new to mac and I assumed that if i was able to find the update threw the software updater that it was safe. Or is this trojan just like a pc virus/malware where it will try and install after clicking a bad link or going to a bad site?
Software Update won't include updates for non-Apple apps. If you get the update notice from already installed software, that should be safe. If, however, you visit a website, like I did this morning, that says you need an updated version of Flash player, don't install it there. Instead, go to Adobe's site directly and download and install the player.To download Flash player: http://get.adobe.com/flashplayer/
To find your currently installed version: http://www.adobe.com/software/flash/about/
Its totally fine.
Just a Jailbreak program on his computer backing up his Cydia blobs
I think,...could be wrong
No, you are quite right, it's the firmware signing address for iPhones. This is completely inert, nothing to see there. AidenShaw is simply demonstrating a lack of knowledge and basic research skills. If this is not enough, check on the website that AidenShaw posted, and read why the address is in the hosts file.
Seeing as the original server is gone, no one has anything to worry about. Macrumours should really update the article to reflect that.
[ Read All Comments ]
 During its teardown of the 2011 Mac Mini's released last month, iFixit discovered plenty of room inside to install a second hard drive. One of our readers discovered the proper process to install...
 Claims of media event and launch dates for the iPhone 5 have quickly accelerated as attention turns toward the window for such an event, which is likely to open in just a few weeks. Just today, a...
 Chinese authorities have discovered another 22 unauthorized Apple resellers in the city of Kunming, according to Reuters. The world's most famous fake Apple Store is also located in Kunming. The...
 iPhoneinCanada.ca reports that employees at Canadian wireless carrier Rogers are currently beginning "pre-launch training" for the iPhone, suggesting that the carrier is preparing its staff...
 Apple has begun shipping Lion USB Recovery Media to some customers, reports 9to5Mac.com.
However, we don't think these aren't the $69 thumb drives that Apple plans to put on sale at...

